
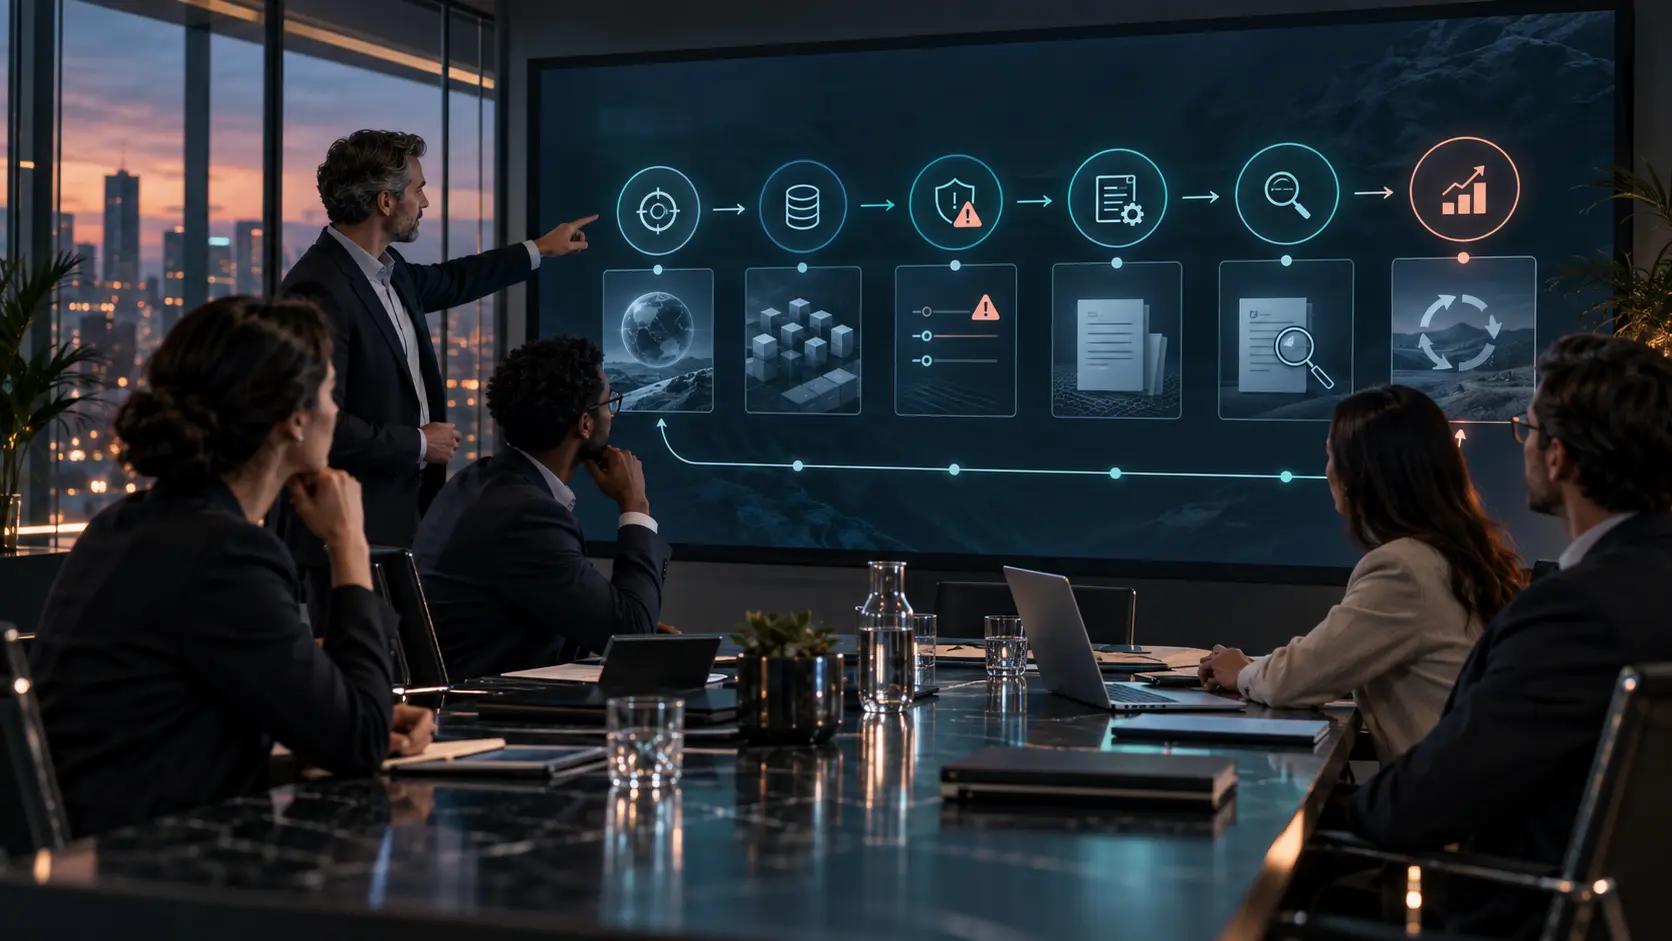
Before you begin: understand the starting point
Two organisations may both want to implement ISO/IEC 42001 while facing completely different situations.
One may use only a few generative AI tools. Another may develop its own models, use recruitment systems, automate decisions or integrate AI solutions from several suppliers.
Implementation should not be identical in both cases. Before designing the AIMS, it is useful to carry out an initial assessment or gap analysis: what do we already have, and what is still missing for a coherent management system?
Existing policies, information-security processes, risk management, data protection, procurement, supplier governance and internal audit arrangements may already provide useful foundations.
Implementing ISO/IEC 42001 does not always mean starting from zero. It means organising what exists, identifying the gaps and building what is genuinely needed.
Step 1. Identify the AI systems
Before an organisation can govern artificial intelligence, it needs to know where that AI is being used.
One of the first practical steps is therefore to create or review the AI systems inventory.
The inventory should not cover only major technology projects. AI may be present in purchased tools, features embedded in existing applications, generative assistants, recruitment, customer service, data analysis, internal developments, pilots and tools adopted directly by individual departments.
For each system, the organisation should know at least its purpose, owner, supplier, users, potentially affected people and context of use.
The first version does not need dozens of fields. It needs enough reliable information to support decisions. The inventory then becomes a point of connection between systems, risks, owners, controls and evidence.
Step 2. Define the context and scope of the AIMS
A common mistake is to attempt to implement ISO/IEC 42001 for ‘all the AI in the business’ without defining what that statement actually means.
The scope needs to be understandable and manageable. The organisation should consider its activities, interested parties, relevant obligations, AI systems, processes and the teams or functions that will participate in the management system.
It can then define the scope of the AIMS. One organisation might begin with AI used in Human Resources, Customer Service and Marketing, together with the corporate processes needed to govern those systems. Another organisation may need a different boundary.
There is no universal scope. It should reflect the organisation’s reality and allow interfaces and dependencies inside and outside the management system to be managed clearly.
Step 3. Assign responsibilities
A management system cannot work if responsibility for AI is dispersed across departments without clear decision rights.
The organisation needs to know who approves new uses, maintains the inventory, assesses risks, reviews suppliers, defines controls, oversees systems, retains evidence, handles incidents, reports to management and monitors the AIMS.
This does not necessarily require a large AI committee. In some organisations a committee will be useful; in others, clearly assigned roles within existing structures will be enough.
The important point is to avoid a familiar situation: everyone is involved, but nobody knows who decides. A sound AI governance model makes those responsibilities visible.
Step 4. Establish the AI policy and objectives
The organisation needs to define how it intends to manage artificial intelligence. The AI policy provides that overall framework.
It should not be a generic statement of good intentions. It must reflect the organisation’s activities and provide a practical reference for decision-making.
Objectives may include maintaining an up-to-date inventory, assessing systems according to risk, reviewing new uses before approval, training relevant roles, improving traceability and periodically reviewing higher-risk systems.
A useful objective should be measurable. ‘Use AI responsibly’ may be a principle. ‘Review every new AI system before it enters use’ can be managed and monitored.
Step 5. Identify risks and opportunities
Risk management is one of the central parts of the system. It should be connected to the actual use of each system rather than becoming a long list of generic threats. Our guide to AI risk management explains this process in more detail.
Consider a tool that recommends candidates for a vacancy. One risk is that characteristics of the system or its data may systematically disadvantage certain profiles.
The organisation should assess probability, impact, affected people, existing controls, additional measures, ownership, residual risk and the criteria used to accept or treat that risk.
Other systems will create very different risks. The inventory and risk process therefore need to remain connected: the organisation should know which system creates each risk and what is being done about it.
Step 6. Select and apply controls
Identifying a risk does not resolve it. The organisation must decide how that risk will be treated.
Controls may be organisational, technical, contractual or procedural. Examples include human review, prior approval, data validation, access control, supplier assessment, system testing, monitoring, change management, intervention mechanisms, decision records and criteria for suspending a system.
Not every system needs the same controls. Proportionality matters. An assistant used to draft internal text does not necessarily require the same level of oversight as a system that influences decisions about people.
The management system should make those distinctions possible and explainable.
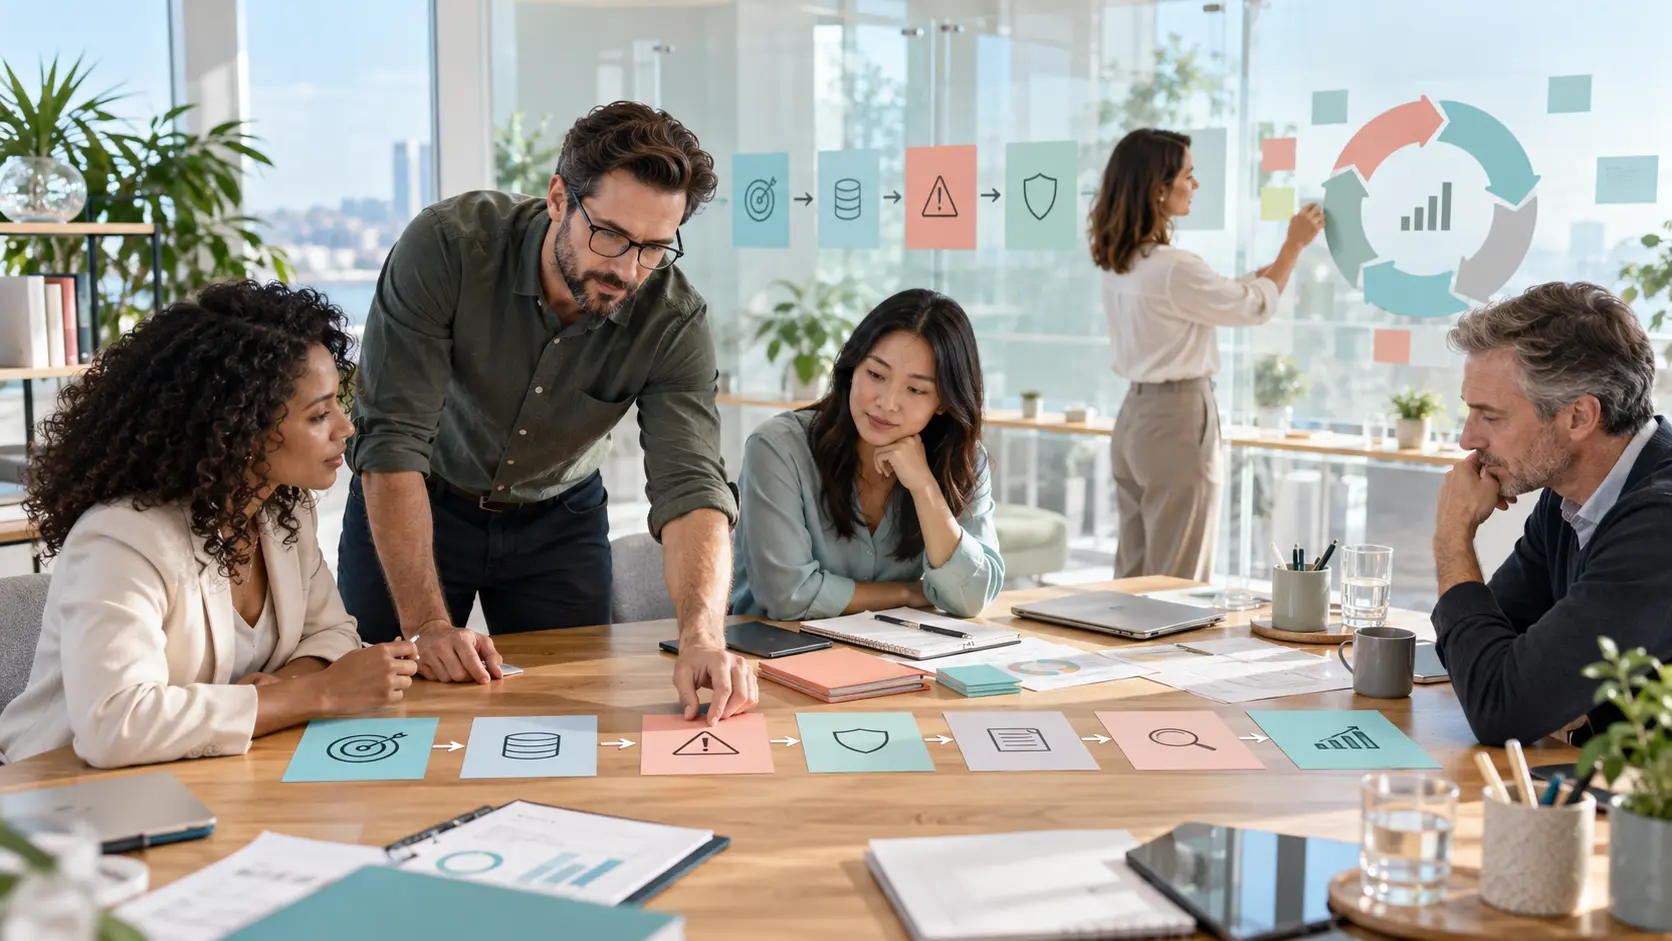
Step 7. Organise documentation and evidence
At this stage, an important question appears: how can the organisation demonstrate that these activities actually took place? This is where AI evidence becomes essential.
A policy states what should happen. A procedure explains how it should happen. Evidence shows that it did happen.
Evidence may include inventory records, risk assessments, approvals, supplier reviews, test results, oversight records, training, incidents, corrective actions, periodic reviews and decisions to accept risk.
The aim is not to retain documents for their own sake. It is to reconstruct what happened, who made a decision and which information supported it.
An organisation with hundreds of disorganised files may have weaker traceability than one with fewer records that are properly structured and connected.
Step 8. Train and raise awareness
ISO/IEC 42001 cannot operate solely through Compliance, Technology or an AI lead. People who use, purchase, develop, supervise or make decisions about AI need to understand their responsibilities.
They do not all need the same training. Procurement may need supplier-assessment criteria. Human Resources may need to understand the risks of particular uses. A technical team may require much more specific knowledge. Management needs enough information to oversee the system and make decisions.
Training should reflect each role rather than becoming another mandatory course that nobody connects with their work.
Step 9. Measure, review and audit the system
Implementing the AIMS does not mean that the project is finished. It means that the organisation can begin managing it.
Indicators may cover systems inventoried, assessments completed, controls outstanding, incidents, reviews, training, corrective actions and new systems entering the scope.
The management system should also be subject to internal audit. Audit should not merely confirm that documents exist; it should assess whether the defined processes actually work and whether the organisation can demonstrate that they work.
Audit results and other performance information allow management to review the AIMS and decide what needs to change.
Step 10. Correct and improve
AI systems change. Suppliers update their products. New uses appear, risks evolve and the regulatory or organisational context may shift.
An AIMS cannot become a static picture of the organisation on the day it was implemented. When a problem is detected, the organisation should analyse it, correct it and, where necessary, prevent it from recurring.
Continual improvement is part of the system’s logic. Implementing ISO/IEC 42001 does not mean reaching a perfect state. It means creating a structure that enables the organisation to detect, decide, act and improve.
How long can implementation take?
There is no single timetable. Duration depends on the organisation’s size, scope, number and complexity of AI systems, existing documentation, maturity, availability of responsible people and integration with other management systems.
An organisation already working with ISO/IEC 27001, ISO 9001 or another management system may be able to reuse processes and structures. Another may need to build many of them from the beginning.
It is therefore better to define the scope and understand the gaps before committing to a timetable.
Common mistakes when implementing ISO/IEC 42001
Starting by writing documents
Creating procedures before understanding the systems and their risks usually produces documentation that is difficult to use.
Trying to do everything at once
Prioritising systems, processes and gaps is more effective than attempting to resolve all AI governance in one project.
Leaving implementation entirely to Technology
AI governance also involves management, business teams, Legal, Procurement, Risk, Security, Privacy and other functions.
Creating an inventory and failing to maintain it
The inventory must evolve when new systems appear or existing systems change.
Confusing implementation with certification
An organisation may implement ISO/IEC 42001 without immediately seeking certification. Certification is a separate assessment performed by a certification body.
Documenting extensively but demonstrating very little
The aim is not to accumulate documents. It is to operate effective processes and retain evidence that shows what happened.
You do not need to do everything at once
ISO/IEC 42001 can look complex when the full standard is considered at once. In practice, it becomes more manageable when it is divided into concrete decisions: which AI do we have, what is in scope, who is accountable, which risks exist, which controls apply, what evidence is retained and how do we know that the system works?
That journey turns the standard into a working management system and allows the organisation to progress gradually.
The objective should not be to build the most complex system possible. It should be to build one that the organisation can use, maintain and improve.
Would you like to understand your organisation’s starting point?
Before implementing ISO/IEC 42001, it is useful to know which elements are already in place, what is missing and where the main gaps lie.
The Céntrika assessment provides an initial view of your organisation’s AI governance, risk and compliance position and helps identify where a deeper review would be useful.
Take the assessment →The assessment provides initial guidance and does not replace a specific evaluation.