
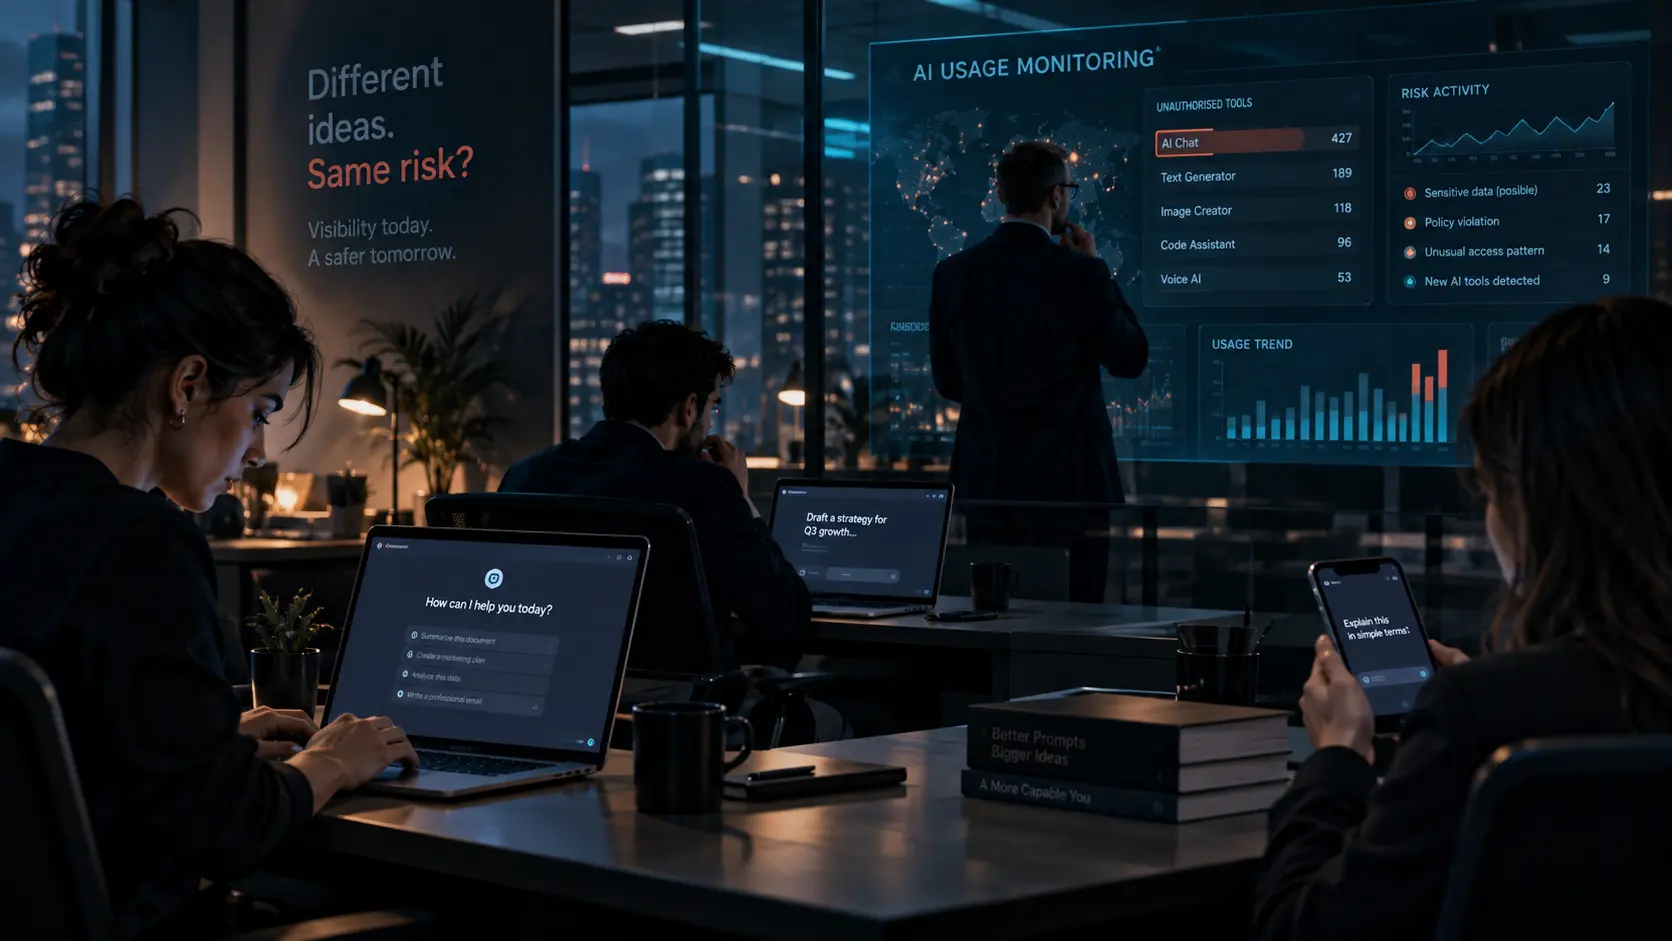
What Shadow AI is
Shadow AI describes tools, models or AI functions that are not identified, registered, approved or assessed through organisational governance.
It may include personal accounts, SaaS tools, extensions, assistants, APIs, local models or AI added to existing software. It is not a legal category under the AI Act and does not necessarily involve malicious or illegal use. The core issue is lost visibility.
Why it appears
Easy access and productivity pressure
Many tools need only an email address, browser or personal card, while staff want to work faster.
Slow approval and weak alternatives
When approval takes months or an AI use policy prohibits tools without offering useful options, informal alternatives appear.
Limited awareness
Users may not understand data, intellectual-property, vendor or internal-policy risks. Shadow AI may therefore reveal a governance gap.
What risks it can introduce
Depending on context, risks may involve personal or confidential data, intellectual property, security, integrations, unverified outputs, affected people and poor traceability.
Regulatory obligations may also arise. Risk comes not simply from the tool, but from purpose, data, context and use within AI risk management.
Shadow AI does not automatically mean non-compliance
An unauthorised tool does not automatically mean an AI Act breach, data-protection violation, security incident or prohibited practice.
The organisation should first examine the tool, use, data, affected people, regulatory role and applicable obligations. Shadow AI is a signal to investigate, not an automatic legal conclusion.
What signals may indicate its presence
Signals include corporate-email accounts, expense-card payments, new extensions, traffic to AI services, unregistered APIs, unknown generated outputs and AI capabilities appearing in approved SaaS products.
Interviews, audits, training, vendor reviews and risk assessments may also reveal use. Discovery need not rely solely on technical surveillance.
How to detect Shadow AI
A practical approach combines:
- the AI inventory and business-unit discussions
- procurement, subscriptions and expenses
- integrations, extensions and APIs
- proportionate security signals
- surveys and AI literacy sessions
- reviews of new capabilities in existing products.
The objective is not a policing operation. It is to restore visibility.
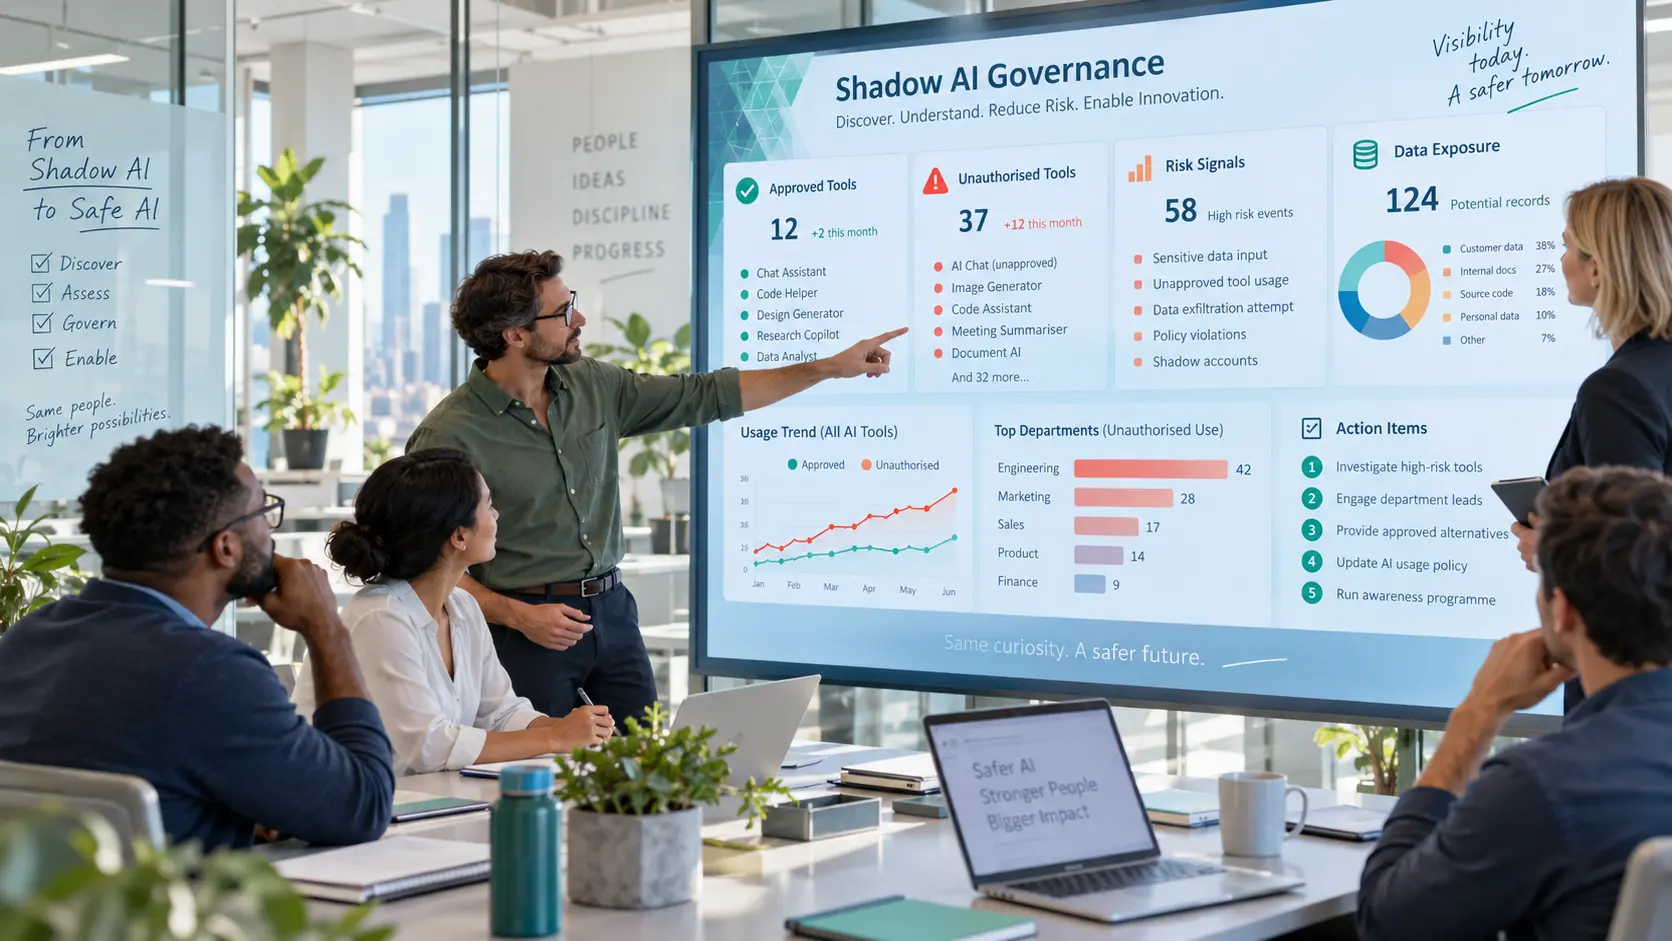
How to assess unauthorised AI use
Avoid both “block everything” and “allow it because people already use it”.
Assess purpose, data, affected people, vendor, system access, risk, approved alternatives and genuine business need. Record the answers in a practical AI register.
When to block, regularise or allow
Block
Where risk conflicts with policy or cannot reasonably be mitigated.
Regularise
Where the use is valuable but needs assessment, contracting, configuration, controls and inventory registration.
Allow with conditions
Limit accounts, data or uses and require human review.
Replace
Offer an approved corporate alternative. The aim is risk reduction while preserving useful work, not maximum blocking.
The role of the AI inventory
A discovered use can become a record covering tool, purpose, owner, vendor, users, data, risk, status and decision.
Status may move from detected — assessment pending to approved with conditions or withdrawn, turning Shadow AI into manageable information.
The role of AI policy and AI literacy
Policy should explain approved tools, approval routes, prohibited data, restricted uses and escalation. AI Act Article 4 requires providers and deployers to take measures supporting AI literacy with regard to knowledge, experience, training and context; it does not require one universal individual level.
Training helps when people understand why rules exist, which risk they address and which alternatives are available.
How to manage generative AI tools
Generative AI governance may cover chatbots, image generators, coding assistants, meeting tools and copilots.
Organisations can maintain approved and restricted lists, prohibited use cases, data rules and human-review requirements. Rules must remain usable.
How to integrate vendors and third parties
Discovered tools may require AI vendor due diligence covering data, security, subprocessors, models, changes, retention, terms and support.
Shadow AI can also arise when an approved product later adds AI. Vendor governance should address changing features and new capabilities.
Evidence and traceability
Record detection date, tool, area, purpose, assessment, decision, controls, owner and review as AI evidence.
Evidence should also support learning: repeated use of one unsanctioned tool may indicate an unmet business need.
How to monitor Shadow AI
Measures may include tools detected, new use cases, exposed areas, tools regularised or withdrawn, related incidents, trained users and authorised-use coverage.
A useful KRI is unauthorised tools accessing sensitive information. A KPI may be detected uses assessed within the defined period. These belong in AI governance KPIs and KRIs, where trend matters more than one figure.
Common mistakes
Prohibiting without alternatives
Use may move further out of sight.
Treating Shadow AI only as cybersecurity
It also concerns data, vendors, compliance, risk and business value.
Monitoring without context
Technical detection does not explain why a tool is used.
Ignoring users or failing to record findings
Real needs are missed and the problem returns.
Failing to update policy
Tools change continuously.
Treating every use as a legal breach
Context must first be assessed within the AI governance framework.
Shadow AI is a visibility problem before it is a prohibition problem
An organisation cannot govern AI that it does not know exists. The first objective is to see; then understand, assess, decide and govern.
An effective flow connects discovery → risk → decision → alternative → monitoring. Shadow AI then becomes a manageable part of AI governance.
References
- Regulation (EU) 2024/1689 — Artificial Intelligence Act.
- Article 4 — AI literacy.
- European Commission — AI Literacy Questions & Answers.
- European Commission — Repository of AI literacy practices.
- ISO/IEC 42001:2023 — Artificial intelligence management system.
- ISO/IEC 23894:2023 — Guidance on AI-related risk management.
These references support literacy, governance, risk and responsible use; they do not make Shadow AI a legal category under the AI Act.
Do you know which AI tools are actually being used in your organisation?
The first step in reducing Shadow AI is regaining visibility over tools, users, data, vendors and risks.
Start the diagnostic →
Céntrika’s diagnostic can help identify that starting point.