
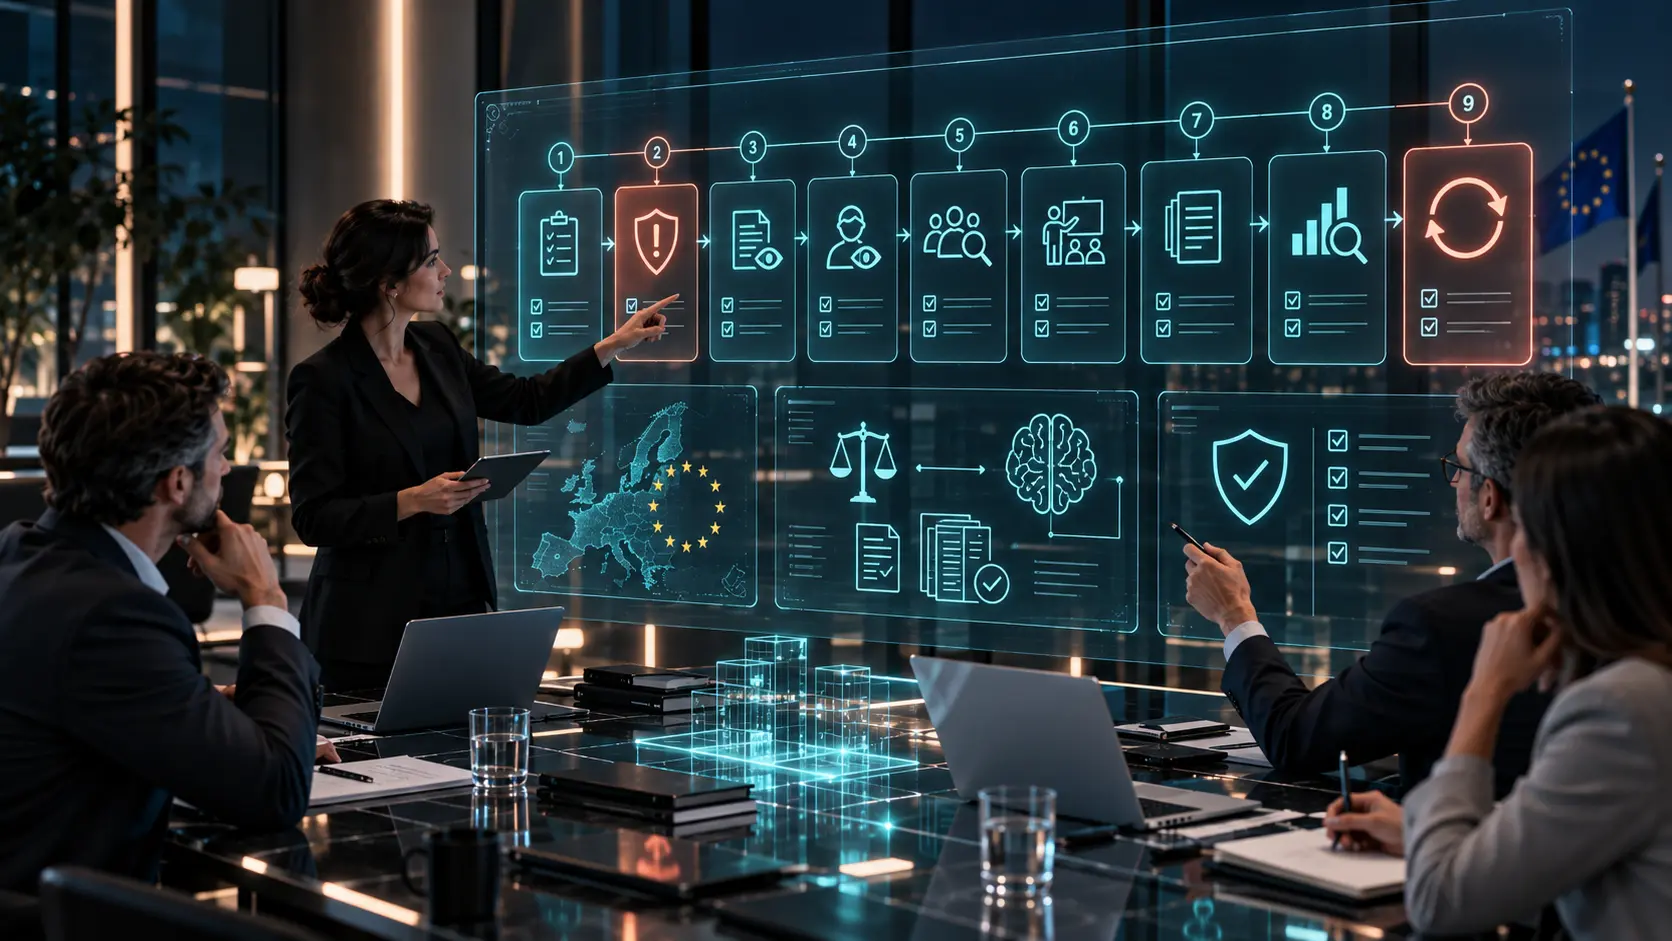
First: understand the business’s role
The EU AI Act assigns different obligations according to the role an organisation performs in relation to an AI system.
A business may be a provider, deployer, importer or distributor, among other roles.
Many organisations purchasing or using third-party solutions will mainly act as deployers. In other words, they use an AI system under their authority in the course of their professional activity.
That classification should not be assumed. A business that substantially modifies a system, changes its intended purpose or introduces certain modifications may find itself in a different position.
The first practical exercise should therefore be simple: for every AI system, identify who provides it and which role the organisation performs.
Identify which AI systems are being used
A business cannot comply properly with the AI Act if it does not know which artificial intelligence it is using.
The starting point should therefore be an AI systems inventory.
It may cover generative assistants, productivity tools, recruitment systems, customer analysis, scoring, automated support, software with embedded AI functions, marketing tools, security systems, supplier solutions and pilot projects.
Not every system will have the same importance, but a reasonable overview makes it possible to classify and prioritise.
For each system, the organisation should know at least its purpose, user department, internal owner, supplier, data used, people potentially affected, level of autonomy, decisions it influences and preliminary classification.
The inventory is not the final objective. It is the basis from which decisions can be made.
Check whether any prohibited practice is involved
Before assessing risk, transparency or documentation, a more basic point should be checked: is the intended use of AI permitted?
The AI Act prohibits certain practices regarded as incompatible with the rights and values protected in the European Union.
Not all of them will affect an ordinary business, but it is sensible to check whether any planned use may fall within these categories.
Areas requiring particular attention include certain manipulative uses, some forms of exploitation of vulnerabilities, certain social-scoring systems and other uses specifically restricted by the Regulation.
These prohibitions already form part of the applicable AI Act framework.
The practical point is straightforward: before putting controls around a system, confirm that the intended use can lawfully take place.
Train the people who use AI
One of the obligations with the broadest organisational reach concerns AI literacy.
Article 4 requires providers and deployers to take measures supporting an appropriate level of AI knowledge and understanding among their staff and other people operating or using AI systems on their behalf.
These AI literacy provisions have applied since 2 February 2025.
This does not mean that everyone must become a specialist. Training should reflect the context, technical knowledge, experience and type of system involved.
For example, a Human Resources team using AI to support recruitment needs to understand different issues from a Marketing team using generative AI to produce drafts.
Training should respond to the risk and the role, rather than being limited to a generic introduction to artificial intelligence.
Review transparency obligations
Since 2 August 2026, the transparency obligations in Article 50 have applied to certain AI systems and uses.
For a business using AI, this may be particularly relevant where it uses emotion-recognition systems, biometric-categorisation systems, systems generating or manipulating deepfakes, or certain AI-generated text published on matters of public interest.
In those circumstances, duties may arise to inform affected people or identify that content has been generated or manipulated using AI.
Not every use of AI automatically creates a transparency obligation. The system and its context of use are what matter.
Identify whether any system may be high-risk
This is one of the most important points.
A business may use many AI systems without any of them being high-risk. It may also have a single system requiring a much stronger level of governance.
Systems connected with sensitive areas such as employment, education, critical infrastructure, biometrics or access to certain services may fall into high-risk categories when they meet the criteria in the Regulation.
The timetable is progressive. Following the amendments adopted in 2026, rules for certain Annex III high-risk systems apply from 2 December 2027, while those for certain systems embedded in regulated products apply from 2 August 2028.
That does not mean waiting until those dates. The preceding period can be used to identify and classify systems, review suppliers, define responsibilities, prepare controls and organise evidence.
Establish human oversight where appropriate
Where a system’s purpose or risk requires it, human oversight must become a real function rather than a general idea.
The organisation should define who oversees the system, what they can review, which information they receive, when they may intervene, when they may stop or correct a decision and how that intervention is recorded.
Human oversight should not exist only in a policy. There must be genuine capacity to act.
A system can have a human in the process and still lack effective oversight if that person does not have enough time, information, authority or training.
Review suppliers and terms of use
Much of the AI used by businesses comes from third parties. Supplier management therefore becomes a central part of compliance.
Before using a solution, it is useful to understand who the supplier is, its intended purpose, the documentation and limitations provided, how changes are managed, which data are used, what support is available, which contractual obligations the supplier accepts and how the customer can meet its own responsibilities.
This is particularly important when the solution is involved in sensitive processes.
Buying AI does not transfer every responsibility to the supplier. The business must still govern how the tool is used within its own organisation.
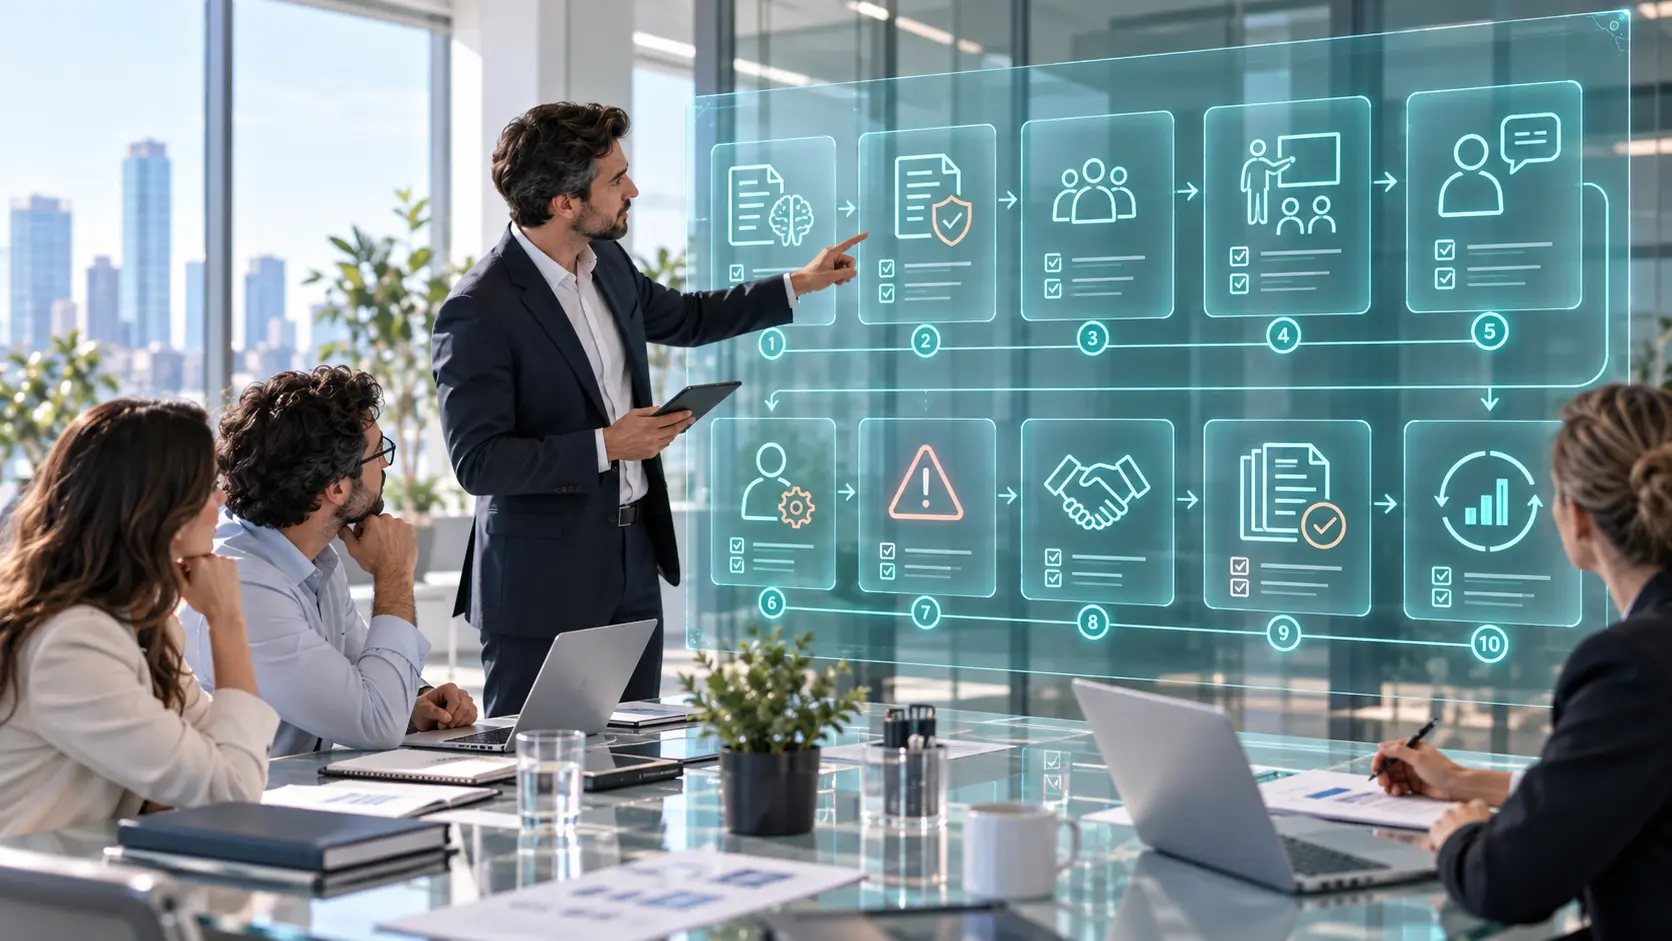
Maintain documentation and evidence
A business may have sound policies and still be unable to show how it actually uses AI.
That is why evidence matters. Depending on the case, it may include an up-to-date inventory, system classification, risk assessment, supplier review, approval decisions, controls, training records, testing, incidents, oversight, reviews, communications to affected people and corrective measures.
The aim is not to generate unnecessary documentation. It is to retain enough information to answer a practical question: which system were we using, for what purpose, who approved it and which controls were in place?
Monitor use and manage incidents
A system’s position does not end when its use is approved.
Suppliers update models, functions change, new users appear, processes are modified and new risks emerge.
Some form of monitoring should therefore exist. It may cover periodic reviews, incidents, significant changes, complaints, deviations, unexpected behaviour, supplier changes and new purposes of use.
If a tool changes materially, an assessment completed months earlier may no longer remain valid.
Integrate AI into internal processes
One of the most common mistakes is to treat the AI Act as an isolated project.
In reality, many obligations should be integrated into processes that already exist.
Procurement can include criteria for assessing AI solutions. Human Resources can define which tools may be used in processes involving people. Security can review access, information and technical dependencies. Data Protection can become involved where personal data are processed. Compliance and Risk can include AI systems in their identification and monitoring processes. Internal Audit can verify that controls genuinely work.
The objective should not be to create a second organisation running in parallel for AI. It should be to incorporate AI governance into the organisation that already exists.
Common mistakes
Common mistakes include assuming that the AI Act affects only developers; treating every AI system as subject to the same obligations; not knowing which AI the organisation uses; relying entirely on the supplier; producing a policy and considering the work complete; and waiting until a regulatory deadline arrives.
Businesses using AI may also have obligations, but the Regulation follows a risk- and role-based approach. Without an inventory, it is difficult to classify, oversee or demonstrate anything. Supplier and deployer responsibilities are not interchangeable, and a policy without processes, owners and evidence has little operational value.
Preparing in advance makes it possible to prioritise and avoid urgent last-minute projects.
Not every business has the same obligations
This is probably the most important message.
The AI Act does not operate as one list of requirements applying equally to every business using ChatGPT, a recruitment system or an industrial algorithm.
Obligations depend on the organisation’s role, the type and purpose of the system, its risk classification, the people affected and the context in which it is used.
The logical sequence should not be to read the whole AI Act and attempt to comply with all of it. It should be: which AI do we use, what role do we have, how is it classified, which obligations apply, which controls do we need and how do we demonstrate them?
That approach turns a complex regulation into a manageable process.
Do you know which obligations may apply to you?
Before designing policies or controls, identify which AI systems your organisation actually uses and which role it performs in relation to each one.
Start the Céntrika assessment →
Use the Céntrika assessment to obtain an initial view of your organisation’s AI governance, risk and compliance.
The assessment provides initial guidance and does not replace a specific legal or technical evaluation.