
What is evidence in AI governance?
A policy may state that every AI system must be assessed before use. That is a rule.
A record showing which system was assessed, when, by whom, which risks were identified and what decision was reached is evidence.
Evidence moves an organisation from saying that it performs a control to being able to show that the control was performed.
The difference between policy, process and evidence
A policy states what the organisation wants to happen. A process explains how it will happen. Evidence shows that it actually happened.
None replaces the others. A policy without execution remains on paper, a process without evidence is difficult to demonstrate and isolated evidence without clear rules may say very little.
Why documentation matters
Organisations change. People move roles, systems evolve and suppliers update their tools. Decisions made today may need to be explained six months from now.
If the answer to ‘Why did we allow this system?’ is only ‘I think Marta reviewed it’, there is a problem. If the assessment, risks, decision and approval can be recovered, the situation is entirely different. That is traceability.
What evidence can an AI system generate?
The answer depends on the system and its context. Not every system needs the same records.
- System record and inventory entry
- Risk assessment and regulatory classification
- Approval for use and supplier review
- Tests and human-oversight records
- Incidents and corrective actions
- Training, meeting minutes and periodic reviews
- Decisions to accept risk
A simple example
Return to the recruitment system. The company says that human oversight is in place. What might demonstrate that?
Useful evidence could include a procedure defining when a person must intervene, a record of reviews of the system’s recommendations, the identity of the responsible person and proof that final decisions are not made automatically.
Evidence must relate to the claim we want to demonstrate. Accumulating files without knowing which question they answer is not enough.
Evidence for risks, controls and decisions
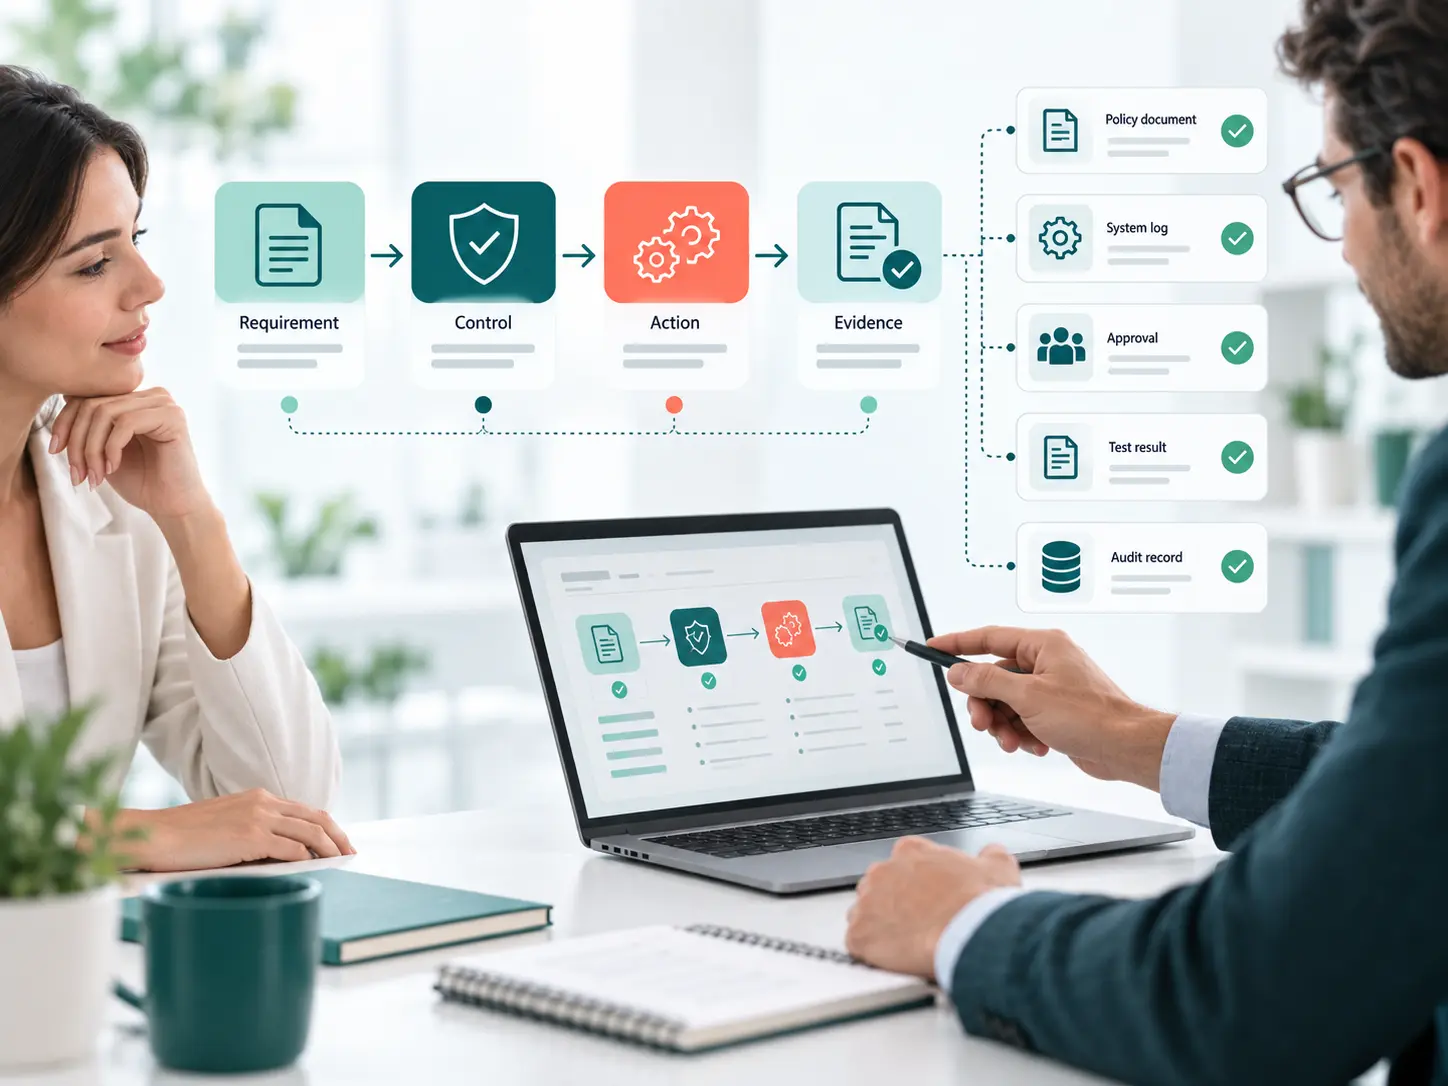
A practical approach connects three things: the risk, the control used to reduce it and the evidence showing that the control was applied.
For example, the risk may be that an incorrect recommendation influences a decision. The control is mandatory human review. The evidence is the review and approval record.
When these three pieces are connected, governance becomes tangible.
How to avoid accumulating documents that serve no purpose
One of the biggest dangers is documenting for the sake of documenting. An organisation may hold hundreds of files and still be unable to explain how it controls AI.
Before creating a record, ask what it is meant to demonstrate. Useful evidence should be relevant, understandable, easy to locate, current and linked to the corresponding system or decision.
Who should retain the evidence?
Evidence may be distributed across IT, Human Resources, Compliance, Procurement and other teams. The problem arises when nobody knows where it is.
The organisation needs a common logic covering what evidence exists, who generates it, where it is kept, for how long and which system it belongs to. The inventory can serve as the point from which key decisions and evidence are located.
Traceability: being able to reconstruct what happened
Traceability does not mean keeping everything forever. It means being able to reconstruct a reasonable history: when the system was introduced, how it was assessed, which risks and controls were identified, who approved it, which incidents occurred and how reviews changed over time.
That is governance — not because a folder is called ‘AI Compliance’, but because the organisation can understand what happened, who decided and why.
A mature organisation is not necessarily the one with the most documents. It is the one that can explain and support its decisions.
Would you like to know which evidence you need?
Start with your systems and their risks. Do not create documentation without a purpose. First identify what you need to demonstrate, then decide which evidence proves it in the simplest way.
Start the Céntrika assessment →
Use the Céntrika assessment to obtain an initial view of your organisation’s AI governance, risk and compliance.
The assessment provides initial guidance and does not replace a specific evaluation.