
What is ISO/IEC 42001?
ISO/IEC 42001 is an international standard for establishing, implementing, maintaining and continually improving an Artificial Intelligence Management System, also known as an AIMS or SGIA.
It is intended for organisations that develop, provide or use AI-based products or services. Its central idea is straightforward: if an organisation uses AI, it should know how that AI is governed — who decides, who is accountable, which risks are reviewed, which controls are applied and what information is retained.
What problem is ISO 42001 trying to solve?
When departments adopt AI independently, basic questions become difficult to answer: who approved each system, which risks were assessed, what data it uses and what happens when it changes?
ISO 42001 provides a common management framework so that AI is not governed through isolated decisions or one-off documents.
What is an Artificial Intelligence Management System?
An AIMS is the set of policies, responsibilities, processes, controls and evidence an organisation uses to manage AI.
It is not a single document or software platform. It connects context, leadership, planning, support, operation, performance evaluation and improvement so that decisions can be repeated, reviewed and demonstrated.
Which organisations can use it?
The standard can be applied by organisations of different sizes and sectors, whether they develop AI, provide AI-based services or use third-party systems.
The scope and level of complexity should reflect the organisation, its role, the systems involved and their risks. A small company does not need to imitate the structure of a multinational.
Where should ISO 42001 implementation begin?
Start with context and scope. Identify why the organisation needs an AIMS, which activities, teams and systems it will cover, and which interested parties and requirements matter.
Leadership, responsibilities and objectives must then be defined. Without ownership, the system will remain a collection of documents rather than a working management system.
The inventory and risks as a starting point
An organisation needs visibility over its AI systems before it can manage them. The inventory links systems with their purposes, owners, data, suppliers, affected people and initial classifications.
From there, risks can be assessed and prioritised. The objective is not to apply every control to every system, but to make proportionate decisions based on context and impact.
What implementing an AIMS really means
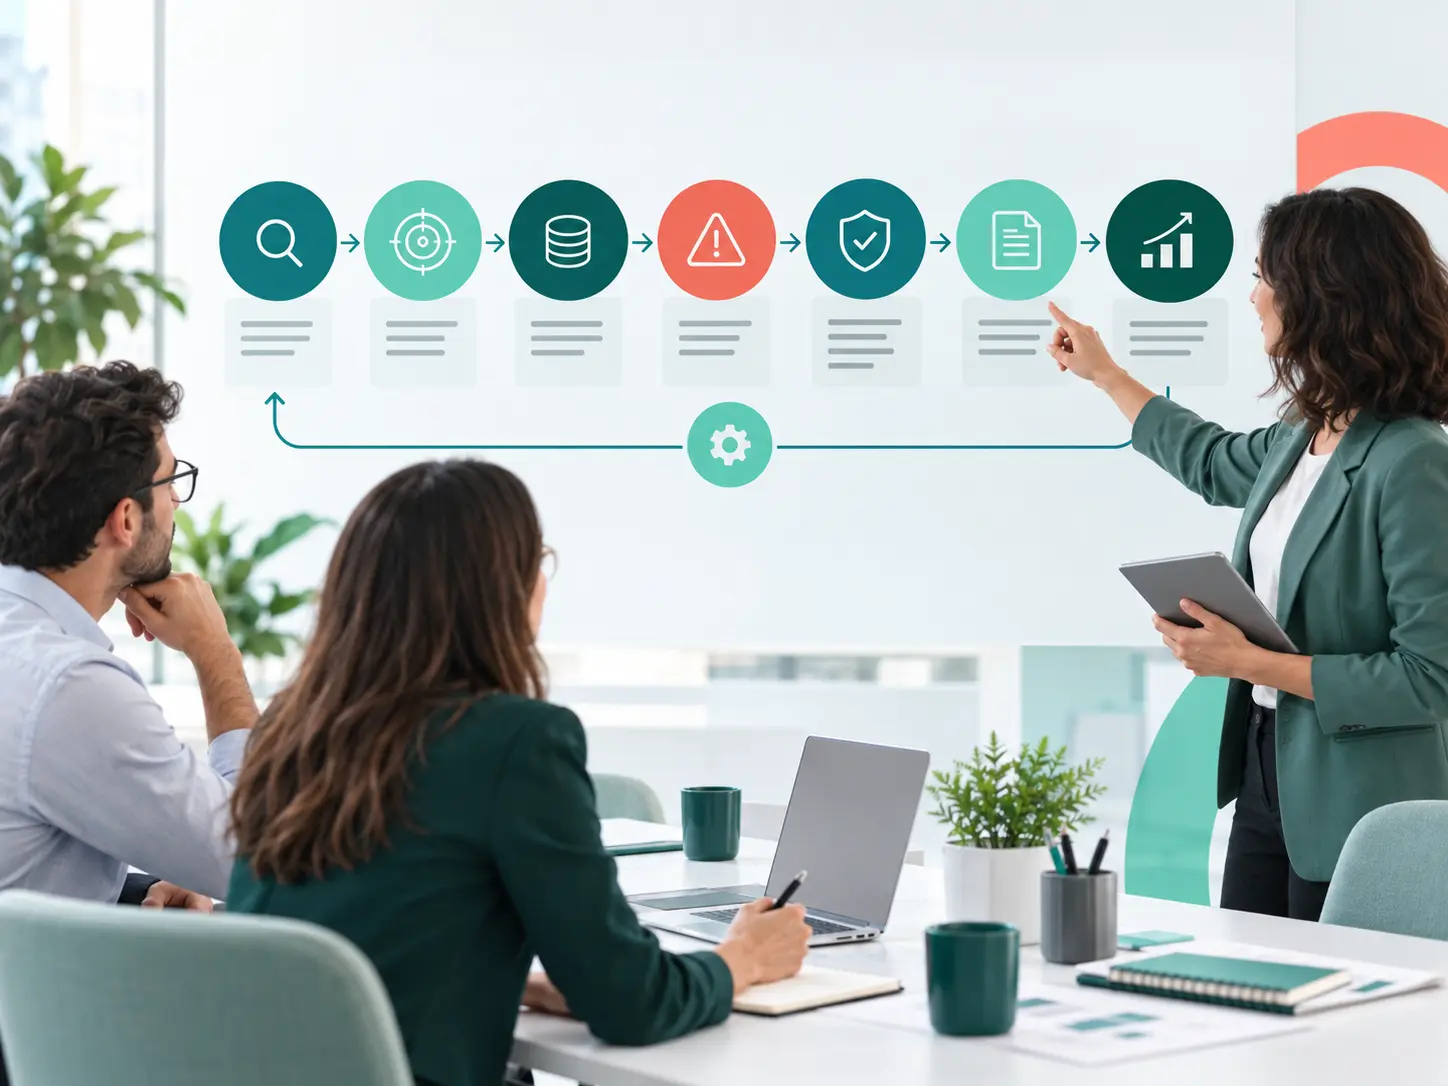
Implementation means turning requirements into normal organisational practice: assigning responsibilities, approving uses, assessing impacts and risks, managing suppliers, monitoring systems, handling incidents, preserving evidence and reviewing performance.
The system should help people make better decisions. If it only produces paperwork, it is not yet working as intended.
Implementing ISO 42001 is not the same as becoming certified
An organisation may implement the standard’s practices without immediately seeking certification. Certification is a separate conformity assessment performed by an accredited certification body.
The first decision should be what level of governance the organisation needs. Certification may then become an objective, but it should not replace the underlying work.
What tends to be hardest during implementation?
The hardest part is rarely writing the policy. It is identifying dispersed systems, agreeing ownership across departments, obtaining reliable information from suppliers, embedding controls into real workflows and keeping evidence current.
That is why a phased approach is usually more sustainable than trying to design the entire system at once.
What should remain after an initial phase?
A useful first phase should leave a defined scope, an initial inventory, assigned responsibilities, a risk assessment method, priority controls, core records and an improvement plan.
It does not need to be perfect. It needs to be understandable, usable and capable of being reviewed.
Would you like to know where you stand before implementation?
Before launching a full AIMS, it can be useful to understand the starting point.
Start the Céntrika assessment →
Use the Céntrika assessment to obtain an initial view of AI governance, risk and compliance and identify the areas requiring most attention.
The assessment provides initial guidance and does not replace a specific AIMS evaluation.