
What is ISO/IEC 42001?
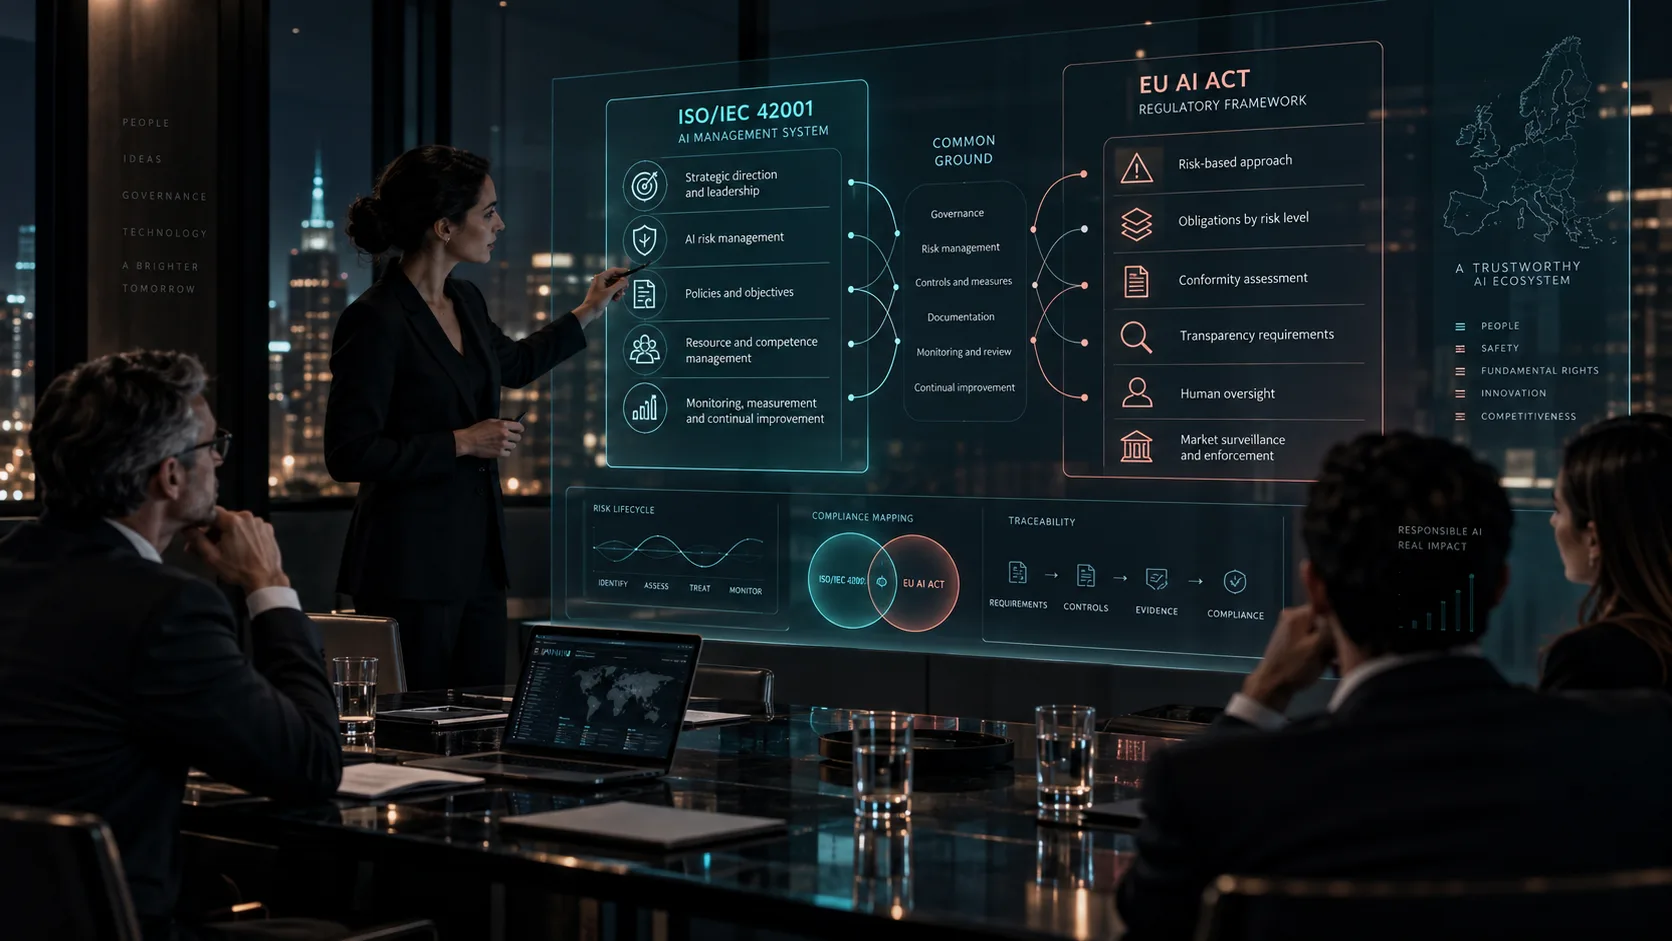
ISO/IEC 42001 is an international standard setting requirements to establish, implement, maintain and continually improve an Artificial Intelligence Management System, or AIMS.
It is not limited to one AI system. It seeks to give the organisation a stable structure for governing how it develops, provides or uses AI.
That management system may cover context and scope, leadership, policies, objectives, responsibilities, risks and opportunities, resources and competence, operational processes, controls, performance evaluation, internal audit, management review and continual improvement.
ISO/IEC 42001 therefore focuses primarily on how an organisation governs its relationship with AI. The guide on implementing ISO/IEC 42001 explains the practical process.
What is the EU AI Act?
The EU AI Act establishes a specific legal framework for artificial intelligence. Its logic is different: it does not create a general corporate management system.
It sets requirements and obligations according to the type of system, intended purpose, risk level, context of use, the organisation's role and the conditions under which it is marketed or used.
The Regulation covers prohibited practices, high-risk AI systems, obligations for certain providers and deployers, transparency, general-purpose AI models, and market surveillance and enforcement.
Its central question is not whether the organisation has a good management system, but which legal obligations apply to this system and this operator? The guide to the AI Act for business provides a broader overview.
The main difference: management system vs regulation
ISO/IEC 42001
Organises how the organisation governs AI.
AI Act
Establishes legal requirements that must be met when the Regulation applies.
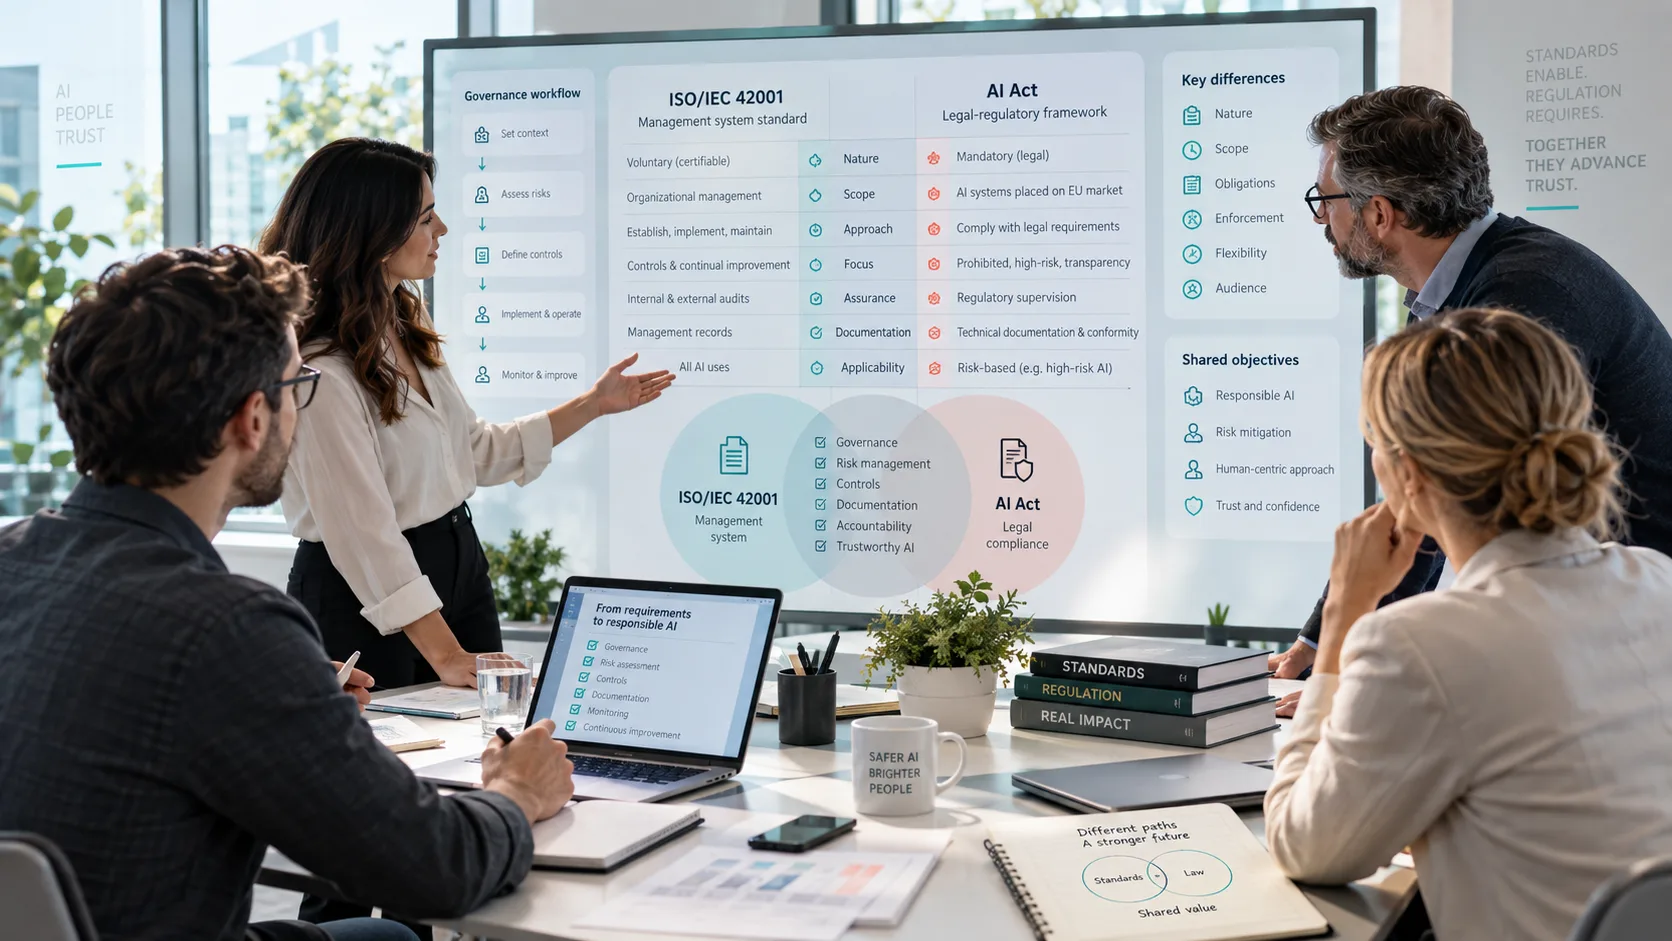
ISO/IEC 42001 operates at organisational and management-system level. The AI Act focuses mainly on systems, uses, risks, operators and specific obligations.
They can therefore work together. ISO/IEC 42001 can structure decision-making, inventory, risk assessment, controls, evidence and performance review. The AI Act determines prohibited practices, high-risk classification, transparency duties, operator obligations and regulatory documentation.
ISO/IEC 42001 is voluntary; the AI Act may be mandatory
ISO/IEC 42001 is voluntary. An organisation may implement it to strengthen governance, assign responsibilities, manage risk, build trust, prepare for certification or integrate AI with other management systems.
The AI Act works differently. When an organisation, system or activity falls within its scope and the relevant conditions are met, applicable legal obligations do not depend on voluntary adoption.
An organisation may choose not to implement ISO/IEC 42001. It cannot choose to ignore applicable AI Act obligations.
Differences in scope
ISO/IEC 42001 can apply to organisations of different sizes and sectors that develop, provide or use AI systems. The AIMS scope can be defined to cover selected processes, units, products or activities.
The AI Act does not operate through a freely chosen organisational scope. Applicability follows the Regulation and requires the organisation to assess whether there is an AI system, its intended purpose, classification, operator role, place of marketing or use, and applicable obligations.
In short: the AIMS scope is defined within the management system; the AI Act's scope is determined legally.
Differences in the risk-based approach
Both frameworks address risk, but not in the same way.
ISO/IEC 42001 requires processes for managing AI-related risks and opportunities within the AIMS. Those risks must be identified, analysed, treated and reviewed systematically.
The AI Act uses a regulatory risk-based approach, with different rules for prohibited practices, certain high-risk AI systems, systems subject to transparency duties and other systems outside those categories.
Organisational risk and legal classification are not equivalent. A system may not be legally high-risk while remaining important because of operational, reputational, economic or human impacts.
Where they overlap
The frameworks overlap in governance, responsibilities, risk management, impact assessment, controls, competence and training, human oversight, documentation, traceability, supplier management, monitoring, incidents, audit and improvement.
ISO/IEC 42001 can provide the organisational structure for managing these activities systematically. The AI Act may supply concrete obligations that the structure must help identify, carry out and demonstrate.
The relationship can be summarised as follows: the AI Act may state what obligation exists; ISO/IEC 42001 can help organise how the organisation manages it.
Governance and responsibilities
Both frameworks value clear responsibilities but approach them differently.
ISO/IEC 42001 requires leadership, assigned responsibilities and a structure for managing the AIMS. The AI Act assigns duties to legally defined operators such as providers and deployers.
These categories must not be confused. An internal AI governance lead does not automatically become an AI Act provider, and an internal system owner is not necessarily the regulatory deployer.
At organisational level, the question is who does what within AI governance. At legal level, it is which role the organisation performs in relation to the system. The guide to roles and responsibilities helps connect the two.
Risk and impact management
ISO/IEC 42001 can place AI risk management within a continuous process. It can also connect with ISO/IEC 23894 and ISO/IEC 42005 for AI impact assessment.
The AI Act contains risk-management requirements for certain systems, particularly high-risk AI systems, and sets specific obligations according to classification and role.
Integration avoids isolated processes: a regulatory risk can enter the internal risk register, while a risk found through the AIMS can trigger a new classification, impact or compliance review.
Controls, documentation and evidence
Policies and procedures are not enough; the organisation must also show that they operate.
ISO/IEC 42001 structures documents, records, decisions, reviews, audits, corrective actions and improvement. The AI Act requires particular documentation, records or information where relevant.
They are not necessarily the same documents, but they can be linked. The AI inventory can identify systems, classification can identify obligations, risk assessment can determine controls and evidence can demonstrate implementation and traceability.
The aim should be to avoid two entirely separate documentation systems where information can legitimately be reused.
How ISO/IEC 42001 can help organise compliance
ISO/IEC 42001 can provide a useful governance structure.
Inventory
Establish a process to identify and maintain AI systems.
Classification
Build in an assessment of each system under the AI Act.
Roles
Define who performs the assessment and who approves the conclusion.
Risks
Integrate regulatory, organisational and human risks.
Controls
Translate identified obligations into specific measures.
Evidence
Define which records must be retained.
Monitoring
Use system changes to trigger reassessment.
Internal audit
Check whether defined processes are genuinely followed.
Improvement
Bring incidents, nonconformities and regulatory change into the improvement cycle.
This integrates the AI Act into the operating model rather than treating it as an isolated legal project.
What ISO/IEC 42001 does not solve on its own
ISO/IEC 42001 does not replace legal analysis of the AI Act.
The organisation must still determine whether a tool is an AI system, whether a prohibited practice exists, whether the system is high-risk, whether Article 6(3) applies, which transparency duties exist, the organisation's role, the specific requirements and applicable dates.
Management system certification does not automatically change a system's legal classification.
Implementing ISO/IEC 42001 can greatly improve readiness and capability, but it does not remove the need to interpret and apply the Regulation correctly.
Does ISO 42001 certification demonstrate AI Act compliance?
This should not be claimed automatically.
ISO/IEC 42001 certification shows that the management system has been assessed against the standard's requirements within a defined scope. The AI Act contains different legal obligations.
AIMS evidence can be valuable in showing that governance, risk management, responsibilities and controls exist. But ISO/IEC 42001 certification and AI Act compliance are not equivalent.
An organisation may hold certification and still need to correct a specific AI Act obligation. It may also meet certain AI Act obligations without ISO/IEC 42001 certification.
Certification does not, by itself, create an automatic presumption of conformity under the AI Act.
How to integrate both frameworks in practice
A practical approach uses two layers.
Layer 1. Governance
ISO/IEC 42001 can provide the stable structure: scope, responsibilities, inventory, risks, controls, training, documentation, audit, review and improvement.
Layer 2. Regulatory requirements
The AI Act supplies specific requirements: classification, prohibited practices, high-risk rules, transparency, operator obligations, documentation, oversight and other applicable requirements.
The layers must then be connected:
AI system → classification → obligations → risks → controls → owners → evidence → monitoring.
This avoids treating ISO and the AI Act as separate projects and allows one governance structure to support multiple needs.
ISO 42001 and the AI Act are not alternative paths
The question should not be “Do we implement ISO/IEC 42001 or comply with the AI Act?”
They address different matters. The AI Act establishes legal obligations; ISO/IEC 42001 provides a management structure.
Used together correctly, they can turn dispersed regulatory requirements into everyday processes, responsibilities, controls and evidence.
The most useful summary is: the AI Act states what must be complied with when applicable; ISO/IEC 42001 helps build an organisation capable of managing it systematically.
References
- ISO/IEC 42001:2023 — Artificial intelligence management system.
- Regulation (EU) 2024/1689 — AI Act.
- ISO/IEC 23894:2023 — Guidance on risk management.
- ISO/IEC 42005:2025 — AI system impact assessment.
Does your organisation manage ISO 42001 and the AI Act within the same governance model?
Before creating separate documentation for each framework, it is useful to understand which AI systems the organisation uses, which obligations apply and which governance processes can already be reused.
Start the diagnostic →
Céntrika’s diagnostic can help identify that starting point.